Compliance articles
Short links carry personal data: IP addresses, device signals, sometimes campaign identifiers tied to a person. These guides cover GDPR-compliant link tracking, EU data residency, cookieless analytics, data processing agreements, and what to ask any vendor before you route customer clicks through them. Written for marketers and DPOs who need practical answers, with the legal sources cited. EU-first is Elido's home turf, and this category is where we show the homework.
 Compliance
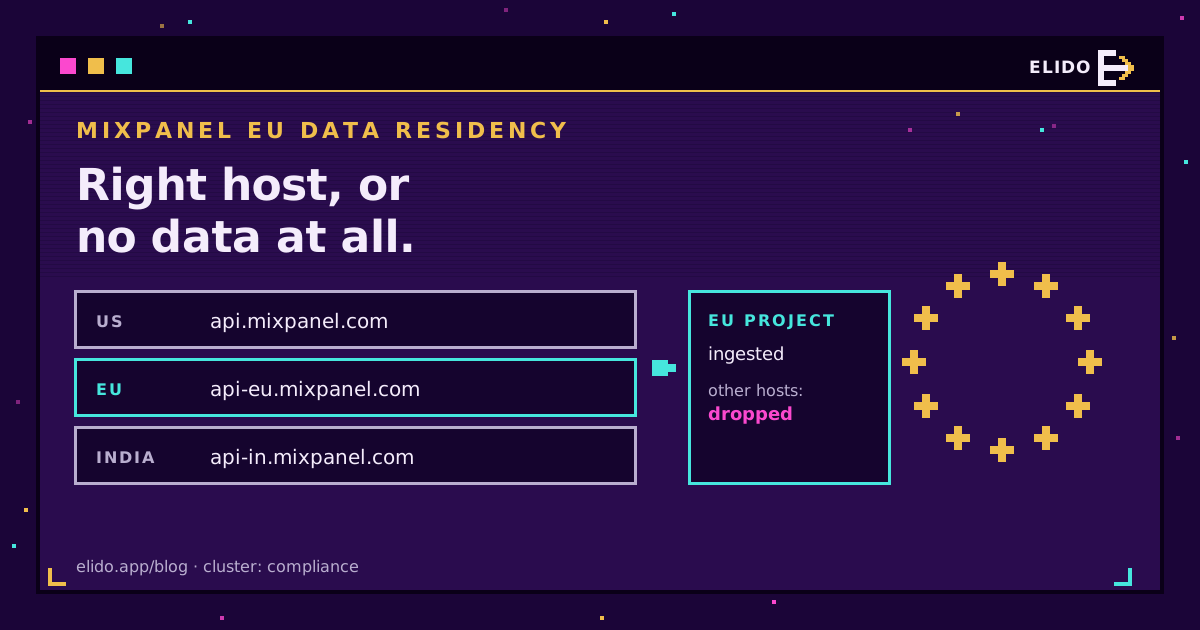
Mixpanel EU Data Residency: Hosts, Dropped Events, GDPR
Mixpanel EU data residency explained: which ingestion host each region uses, why events sent to the wrong one vanish, and what it means for GDPR transfers.
8 min read Compliance
Homograph Attack: Spot Punycode and Lookalike Domains
A homograph attack swaps look-alike characters into a domain, and punycode (xn--) is how it travels. Here is how to spot one before you click.
7 min read Compliance
QR Code Accessibility: WCAG, Contrast and Alternatives
A QR code is an image with no text alternative and a target nobody can tab to. What accessibility rules expect, and the printed fallback that fixes most of it.
7 min read Compliance
Click Data Retention: How Long to Keep Link Analytics
GDPR gives no number for click data. How to set retention windows per data class, what Elido stores today, and how to delete without losing reporting.
7 min read Compliance
QR Codes and GDPR: What a Scan Collects and What You Owe
QR codes and GDPR: the printed code collects nothing, the redirect processes an IP address, which is personal data. What that means for basis and retention.
7 min read Compliance
Digital Product Passport QR Code: What the ESPR Requires
A digital product passport needs a data carrier, not a QR code by name. What the ESPR says, the February battery deadline, and where a durable QR resolver fits.
6 min read Compliance
Cookie Consent for Short Links: What the EU Requires
Need cookie consent for short links? A DPO explains when redirect tracking triggers ePrivacy consent, and when a cookieless setup with EU storage avoids it.
7 min read Compliance
Is Google Analytics GDPR Compliant? EU Answer
Is Google Analytics GDPR compliant? It is not banned, but EU regulators ruled it broke GDPR by sending data to the US. What changed since, and what to do.
5 min read Compliance
Is Bitly GDPR Compliant? A DPO's Honest Answer
Is Bitly GDPR compliant? It has a DPA, SCCs and Data Privacy Framework certification. Compliant, yes, but not the same as EU-only data residency.
7 min read Compliance
EU Alternatives to US SaaS: A Vendor-Checked Guide
EU alternatives to US SaaS, checked against vendor pages: who is actually European, the CLOUD Act vs GDPR conflict, and a five-question test for any tool.
7 min read Compliance
Are QR Codes Safe? Quishing and How to Stay Protected
QR codes are safe to scan - the risk is where they lead. How quishing works, how to spot a malicious QR code, and what to do if you scanned a fake one.
7 min read Compliance
Are URL Shorteners Safe? What Scanning Does and Misses
Reputable URL shorteners are safe, but a redirect can hide a bad destination. What provider scanning catches, what it misses, and how to check a link.
8 min read CornerstoneCompliance
GDPR for URL shorteners: what your DPO actually wants to see
A working DPO's read on the GDPR articles that apply to URL shorteners - Articles 3, 6, 28, 30, 32, 35, sub-processor disclosure, and the DPA clauses
15 min read Compliance
SOC 2 and HIPAA for a URL Shortener: What to Ask For
Elido has no SOC 2 report or ISO 27001 yet. What a buyer should request from any URL shortener for SOC 2 and HIPAA, and what Elido can show today.
6 min read Compliance
Consent Mode v2 for link tracking: what the DMA changed
Consent Mode v2 and the Digital Markets Act rewrote short-link analytics: what the four signals mean, how server-side recovery works.
13 min read Compliance
Schrems II and Tracking Pixels: Where the DPF Leaves You
Schrems II killed Privacy Shield; the EU-US Data Privacy Framework restored adequacy in 2023. What that means for tracking pixels under GDPR Article 44+.
12 min read Compliance
EU data residency for marketing tools: a DPO checklist
What EU data residency covers for link tracking and conversion forwarding, where marketing stacks leak EU data, and eight answers to get from vendors.
9 min read Compliance
Cookieless Attribution Explained: What Still Works
Third-party cookies are fading and script-set cookies expire fast. Which attribution paths still hold, what they cost you, and where consent still applies.
9 min read Compliance
Safari ITP and click attribution in 2026: what still works
Every ITP version broke another tracking workaround. The full timeline, what each change killed, and the server-side redirect pattern that survives them all.
12 min read Compliance
URL shortener security checklist: 10 controls to verify
Ten security controls to check before you trust a URL shortener: threat-feed scanning, signed webhooks, key hashing, rate limits, audit logs and takedowns.
7 min read Compliance
GDPR-Friendly URL Shortener: 10 Checks Before You Sign
A GDPR-friendly URL shortener needs a DPA, minimal click data, erasure and no pixels at redirect. Ten contract checks, and where Elido falls short.
8 min read